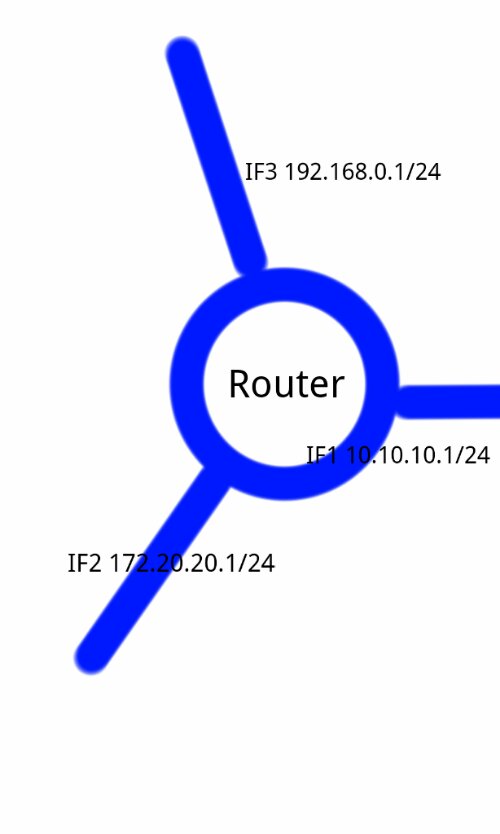
Here’s the question: in the above example, is it possible (using classic NAT, not NAT Virtual Interface) to translate traffic coming in on Interface1 (though not necessarily with that network as its source address) to have a source IP on Interface2 (172.20.20.6, for example) and then send it out Interface3, where it will match a crypto map and be subject to IPSec encapsulation, all without ever having traversed Interface2?